Worm Update #2
Tuesday, April 17, 2007
Symantec has added a new designation for the Rinbot described earlier, W32.Rinbot.BC. They also say that, "Virus definitions dated April 16, 2007 or earlier may detect this threat as W32.Rinbot.A", which is utter crap -- as of the outbreak yesterday, their signatures didn't detect it as anything. After some newer releases arrived in the afternoon, suddenly it was recognized as Rinbot.A, and only now as the new variant.
The bottom line? Signature-based scanners are losing their effectiveness, and fast.
- David
posted by David @ 11:30 AM,
,

Dodging Bullets, Take One
Thursday, December 21, 2006
An object lesson in keeping software patched and updated:
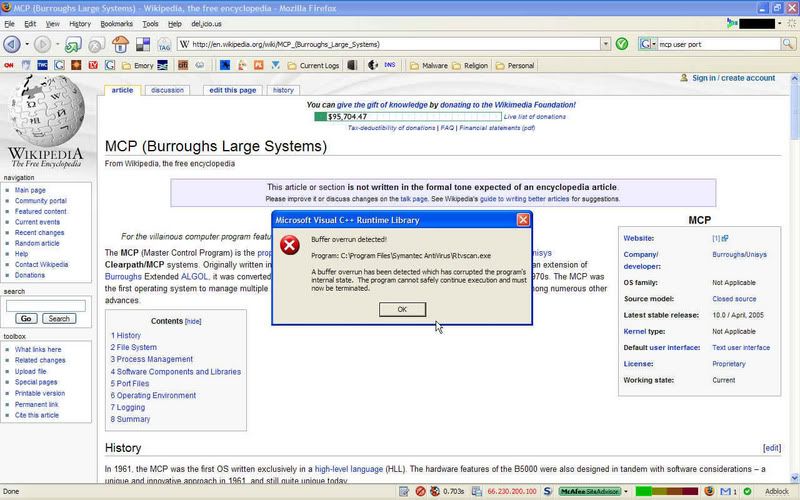 I saved that screenshot in a newly-created directory labeled "Oh Crap," and as soon as I saw the message, I knew what was in-progress: this vulnerability, fixed in the 10.1.x versions of Symantec Client Security. Too bad I had been too lazy to update from 10.0.x...
For most people, such a turn of events would've had their computer either attacking others on its own (i.e. the recent Big Yellow worm) or as part of a hacker-controlled botnet. Thankfully, I usually put a lot of time and effort into my security, and the excellent Sunbelt-Kerio Personal Firewall that I have in place of the craptacular Windows Firewall caught the exploit in the act:
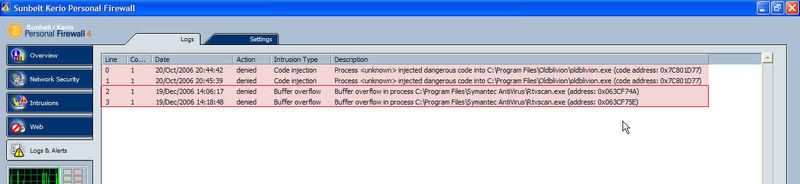 ...and all I had to show for it was some log entries, a network-wide alert, a crashed Symantec session, and a quick RootkitRevealer scan to ensure nothing had been activated that WinPatrol Plus, Sunbelt-Kerio, and Symantec were unable to see. One bullet dodged, one lesson learned.
~ Nexus7
Labels: exploit, symantec, worm
posted by David @ 9:42 PM,
,
